Security operations
Explore the latest insights, tools, frameworks, and developments in security operations (SecOps).
Filtered by
Security operations
Refine results
Sort By
Content Type
Topic
Threat intelligence
Products and services
Publish date
-
Microsoft is excited to be named an Overall Leader, and the Market Leader in the Kuppinger Cole Analyst’s 2026 Emerging AI Security Operations Center (SOC) report, as we see automation and AI as core components of the future of cybersecurity. -
8 best practices for CISOs conducting risk reviews
Embracing strong proactive security is something we can all do to mitigate our increased exposure to security threats. -
The agentic SOC—Rethinking SecOps for the next decade
In the SOC of the future, autonomous defense moves at machine speed, agents add context and coordination, and humans focus on judgment, risk, and outcomes. -
Help on the line: How a Microsoft Teams support call led to compromise
A DART investigation into a Microsoft Teams voice phishing attack shows how deception and trusted tools can enable identity-led intrusions and how to stop them. -
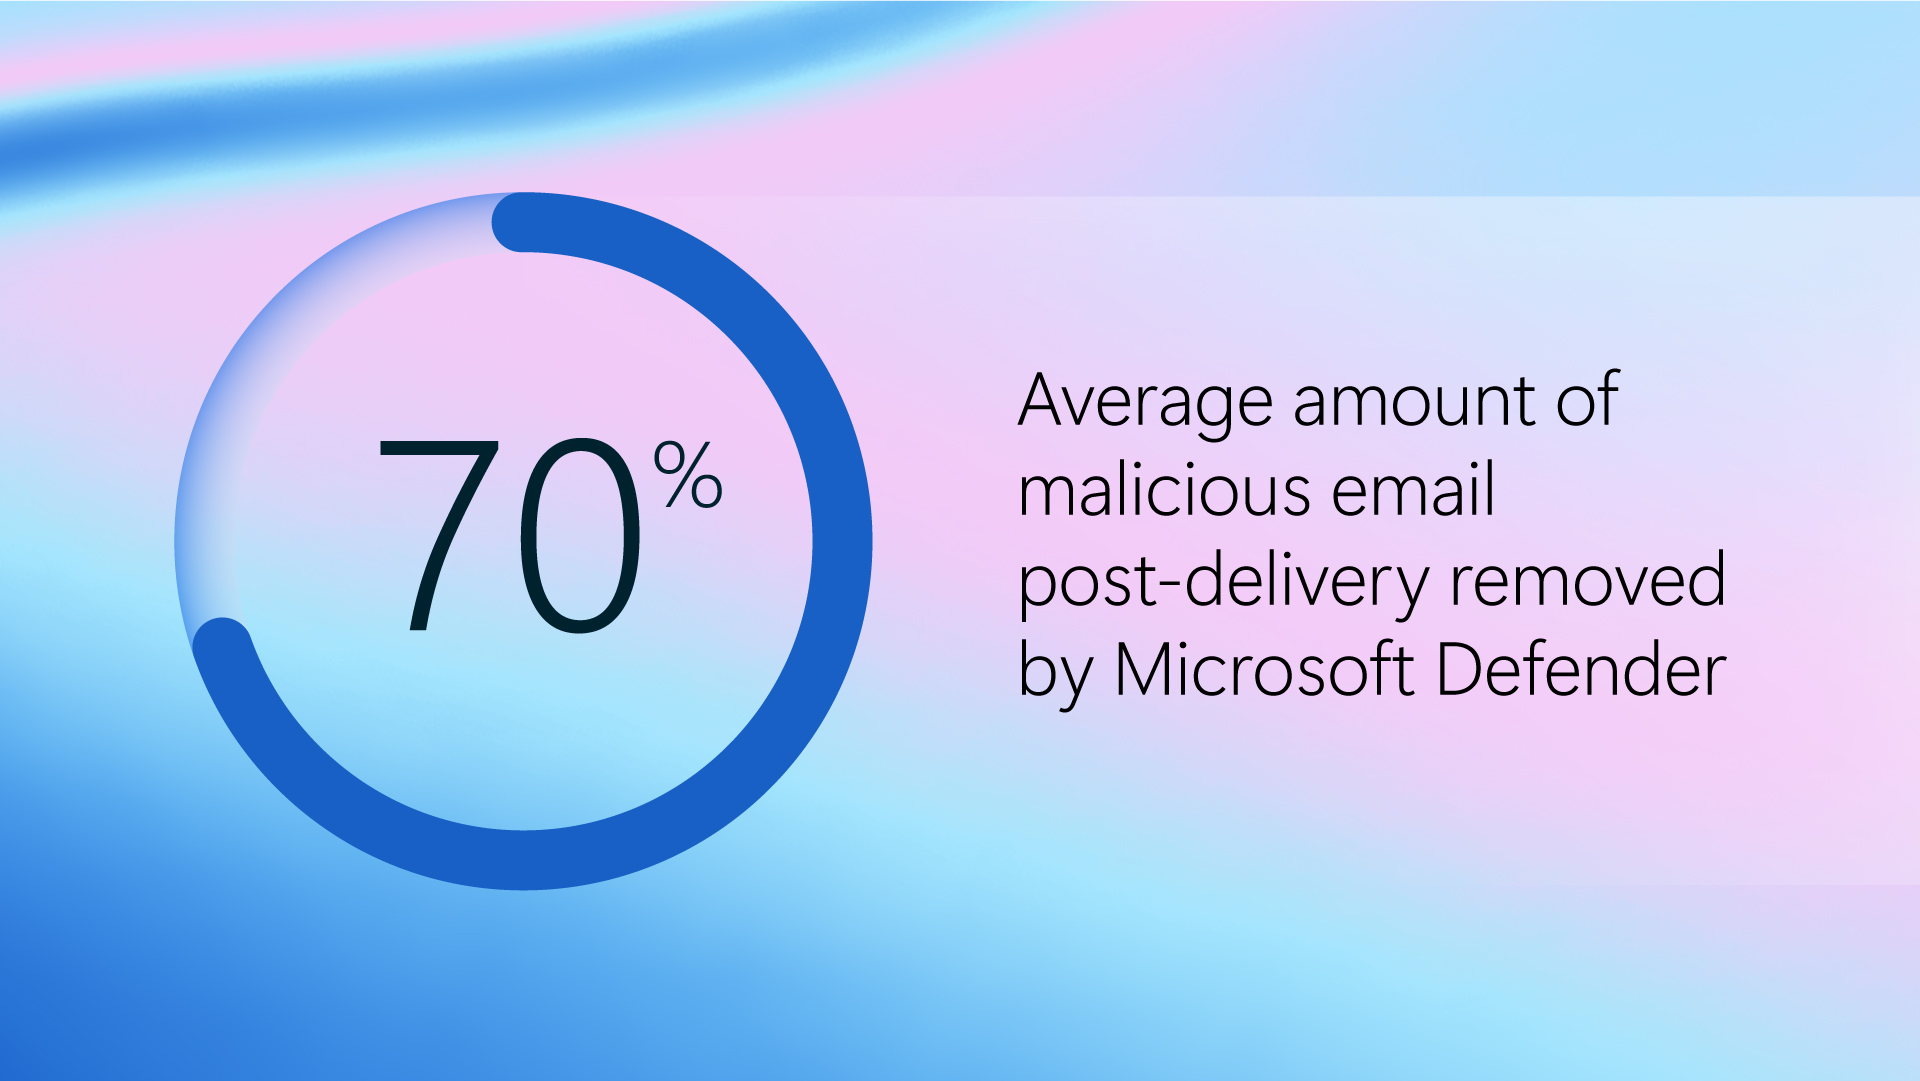
From transparency to action: What the latest Microsoft email security benchmark reveals
The latest Microsoft benchmarking data reveals how Microsoft Defender mitigates modern email threats compared to SEG and ICES vendors. -
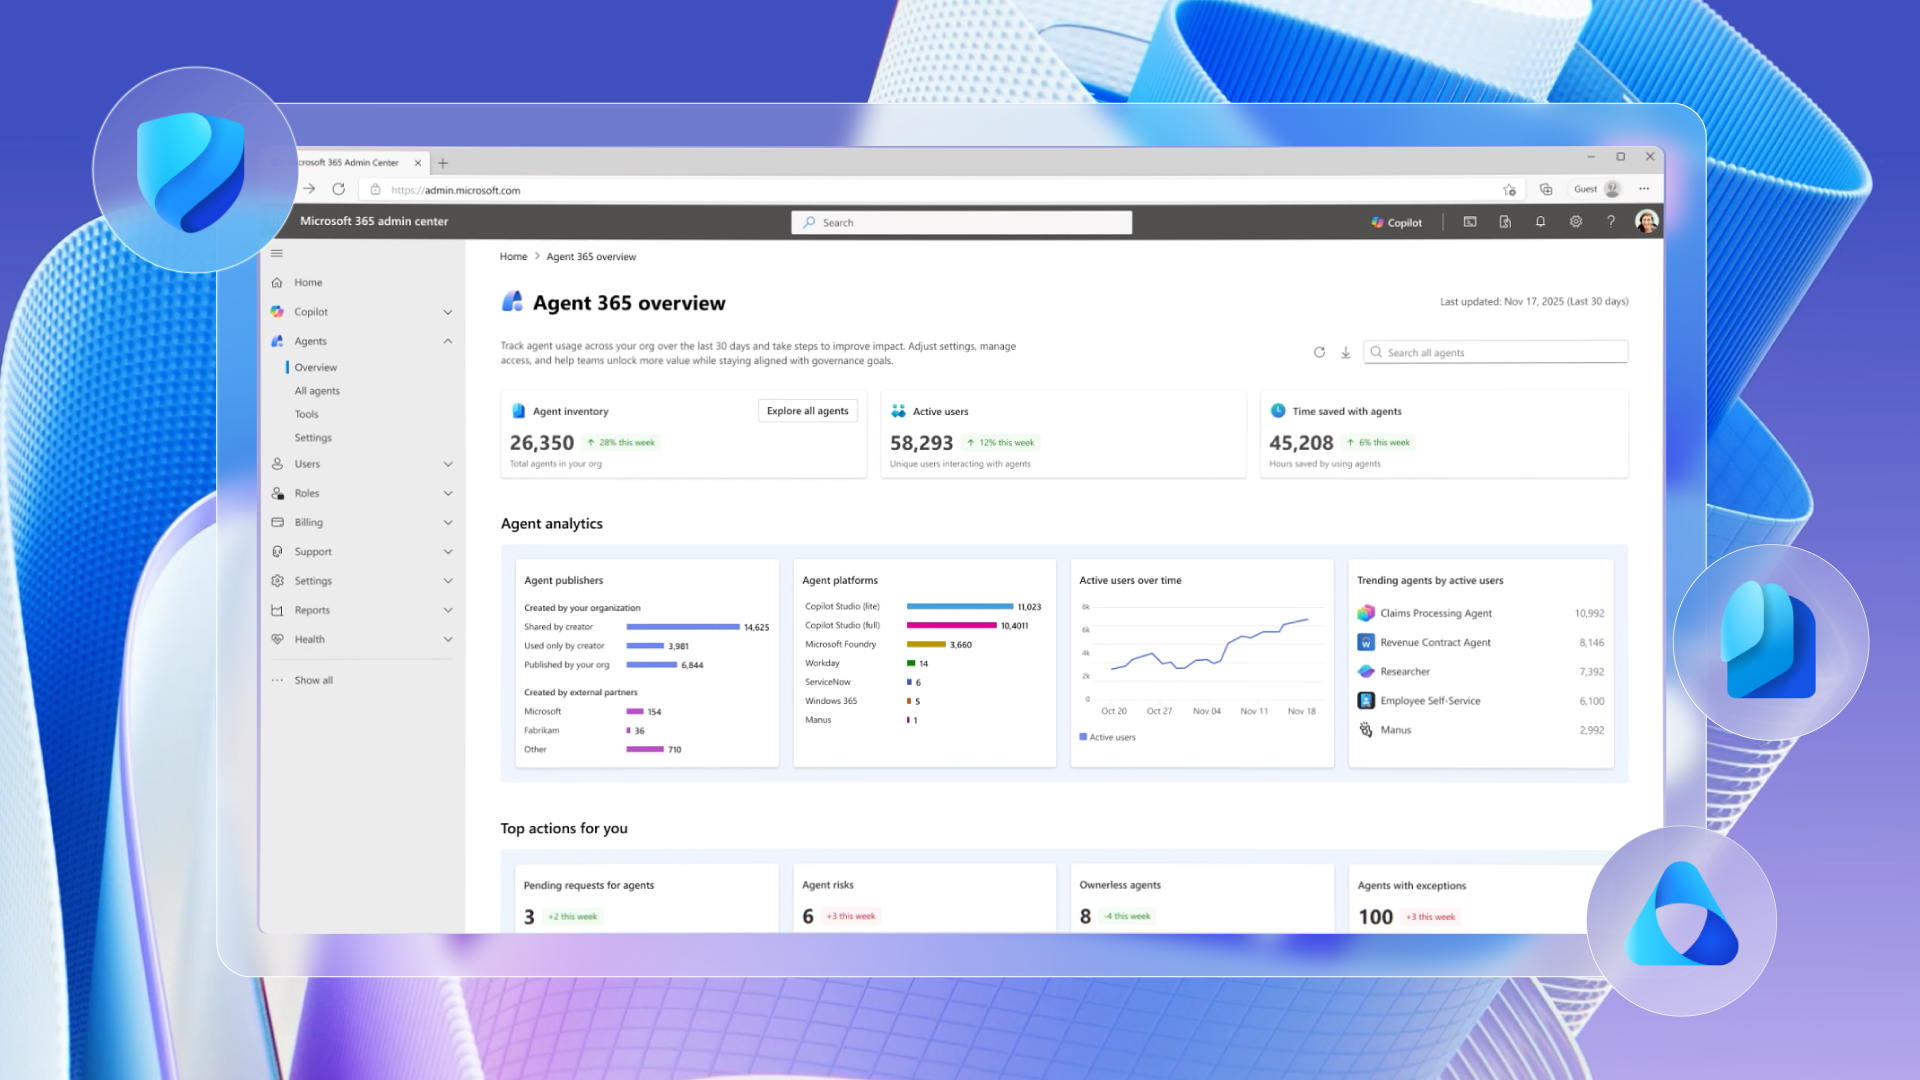
Secure agentic AI for your Frontier Transformation
We are announcing the next step to make Frontier Transformation real for customers across every industry with Wave 3 of Microsoft 365 Copilot, Microsoft Agent 365, and Microsoft 365 E7: The Frontier Suite. -
Women’s History Month: Encouraging women in cybersecurity at every career stage
This Women’s History Month, we explore ways to support the next generation of female defenders at every career stage. -
Threat modeling AI applications
AI threat modeling helps teams identify misuse, emergent risk, and failure modes in probabilistic and agentic AI systems. -
Scaling security operations with Microsoft Defender autonomous defense and expert-led services
AI-powered cyberattacks outpace aging SOC tools, and this new guide explains why manual defense fails and how autonomous, expert-led security transforms modern protection. -
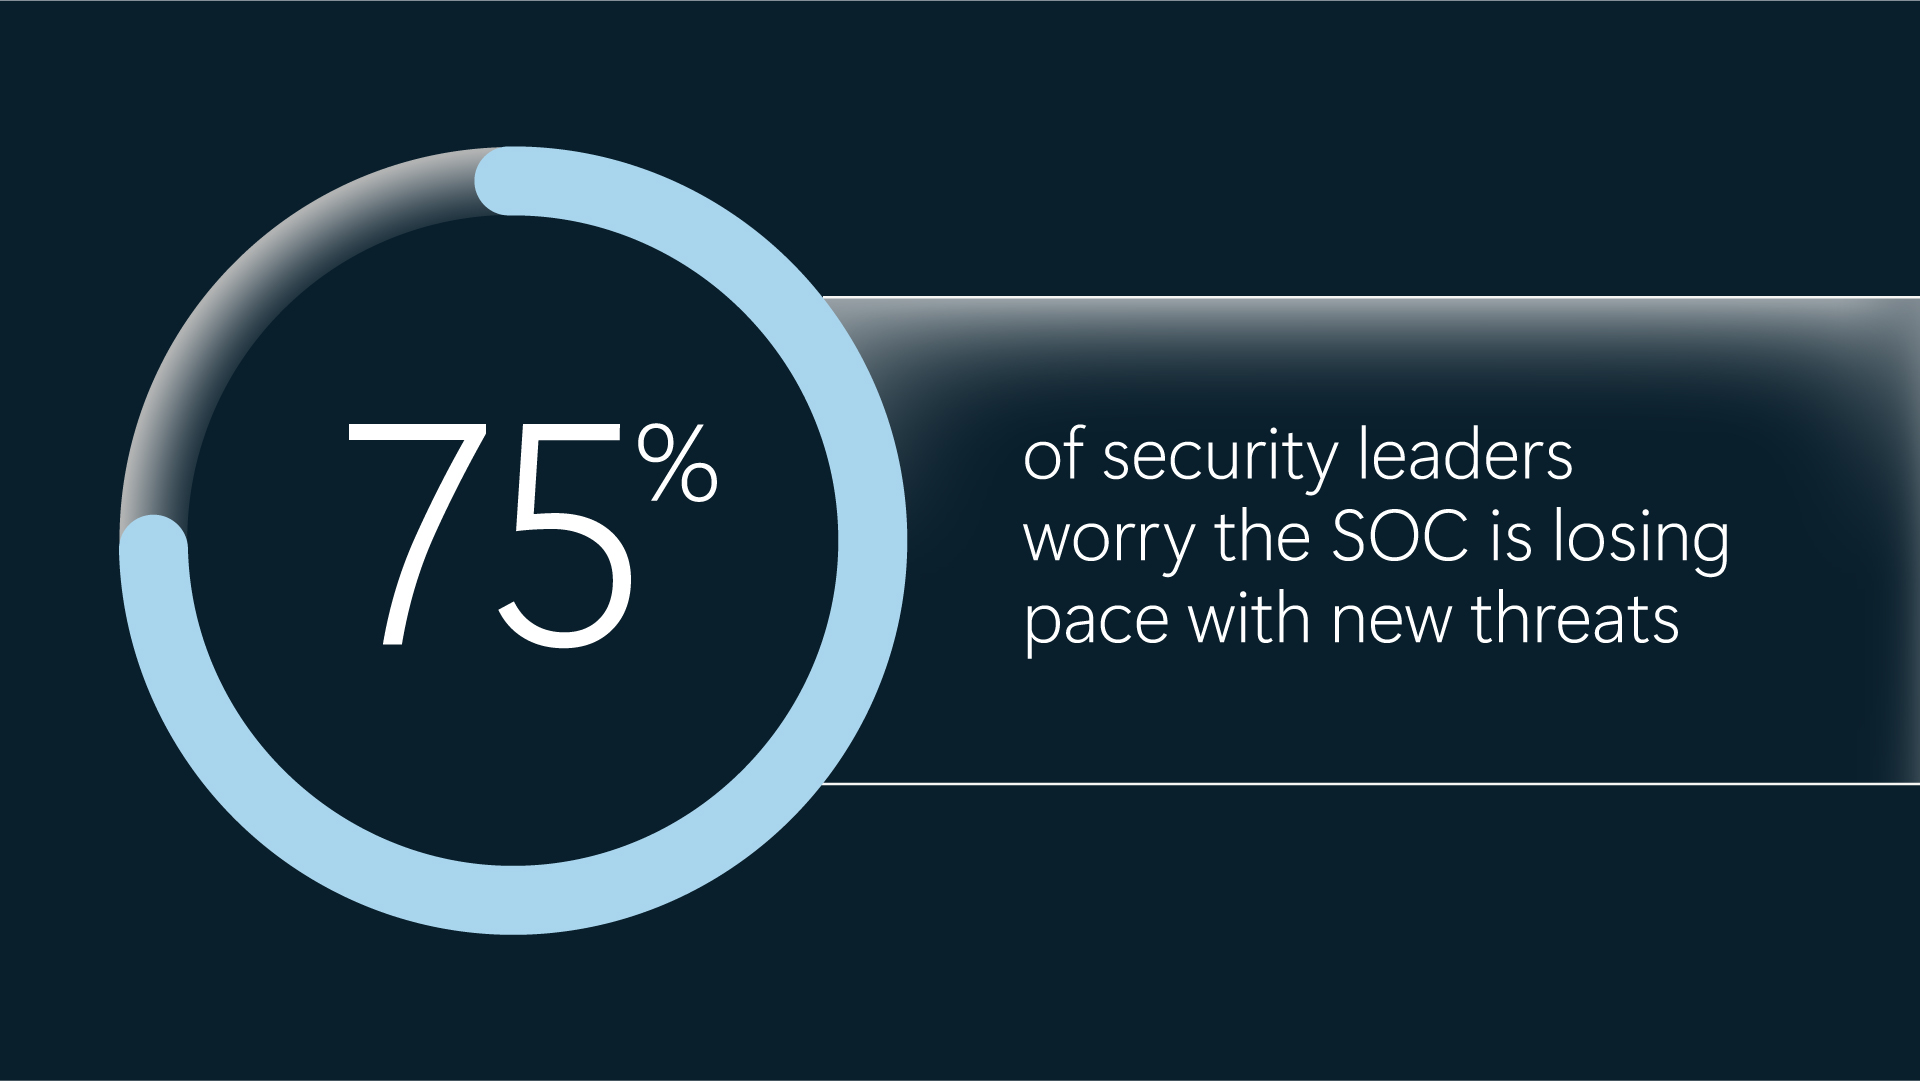
Unify now or pay later: New research exposes the operational cost of a fragmented SOC
New research from Microsoft and Omdia reveals how fragmented tools, manual workflows, and alert overload are pushing SOCs to a breaking point. -
The strategic SIEM buyer’s guide: Choosing an AI-ready platform for the agentic era
New guide details how a unified, AI ready SIEM platform empowers security leaders to operate at the speed of AI, strengthen resilience, accelerate detection and response, and more. -
The security implementation gap: Why Microsoft is supporting Operation Winter SHIELD
Most security incidents happen in the gap between knowing what matters and actually implementing security controls consistently.